Reverse-Engineering 2
Process analysis tooling, network isolation for safe dynamic analysis, packers and unpacking strategies.
Deep-dive posts, investigations, and walkthroughs focused on defenders, learners, and tinkerers. No fluff—just practical knowledge and repeatable steps.
Process analysis tooling, network isolation for safe dynamic analysis, packers and unpacking strategies.
Topologies, IP addressing, DNS, TCP/UDP, NAT, and troubleshooting fundamentals.
Sessions, processes, and services—mapped to how Windows actually runs.
Trace pfSense and Snort connectivity failures, investigate false positives, and tune narrow exceptions while preserving useful detection.
Diagnose Proxmox wireless networking and choose between Ethernet, a wireless bridge device, or a routed guest network.
Distinguish initramfs, root-device, filesystem, and disk failures, then recover an ext4 Linux installation safely.
Use PowerShell to separate DHCP, gateway, DNS, and application failures without repeatedly resetting the Windows network stack.
Diagnose Remote Desktop sound and microphone failures through client settings, session policy, devices, and application selection.
Use PowerShell, queue inspection, and event logs to distinguish printer hardware, connectivity, driver, and spooler problems.
Inspect Microsoft Defender state, use the correct MpCmdRun executable, repair intelligence updates, and verify scans without bypassing policy.
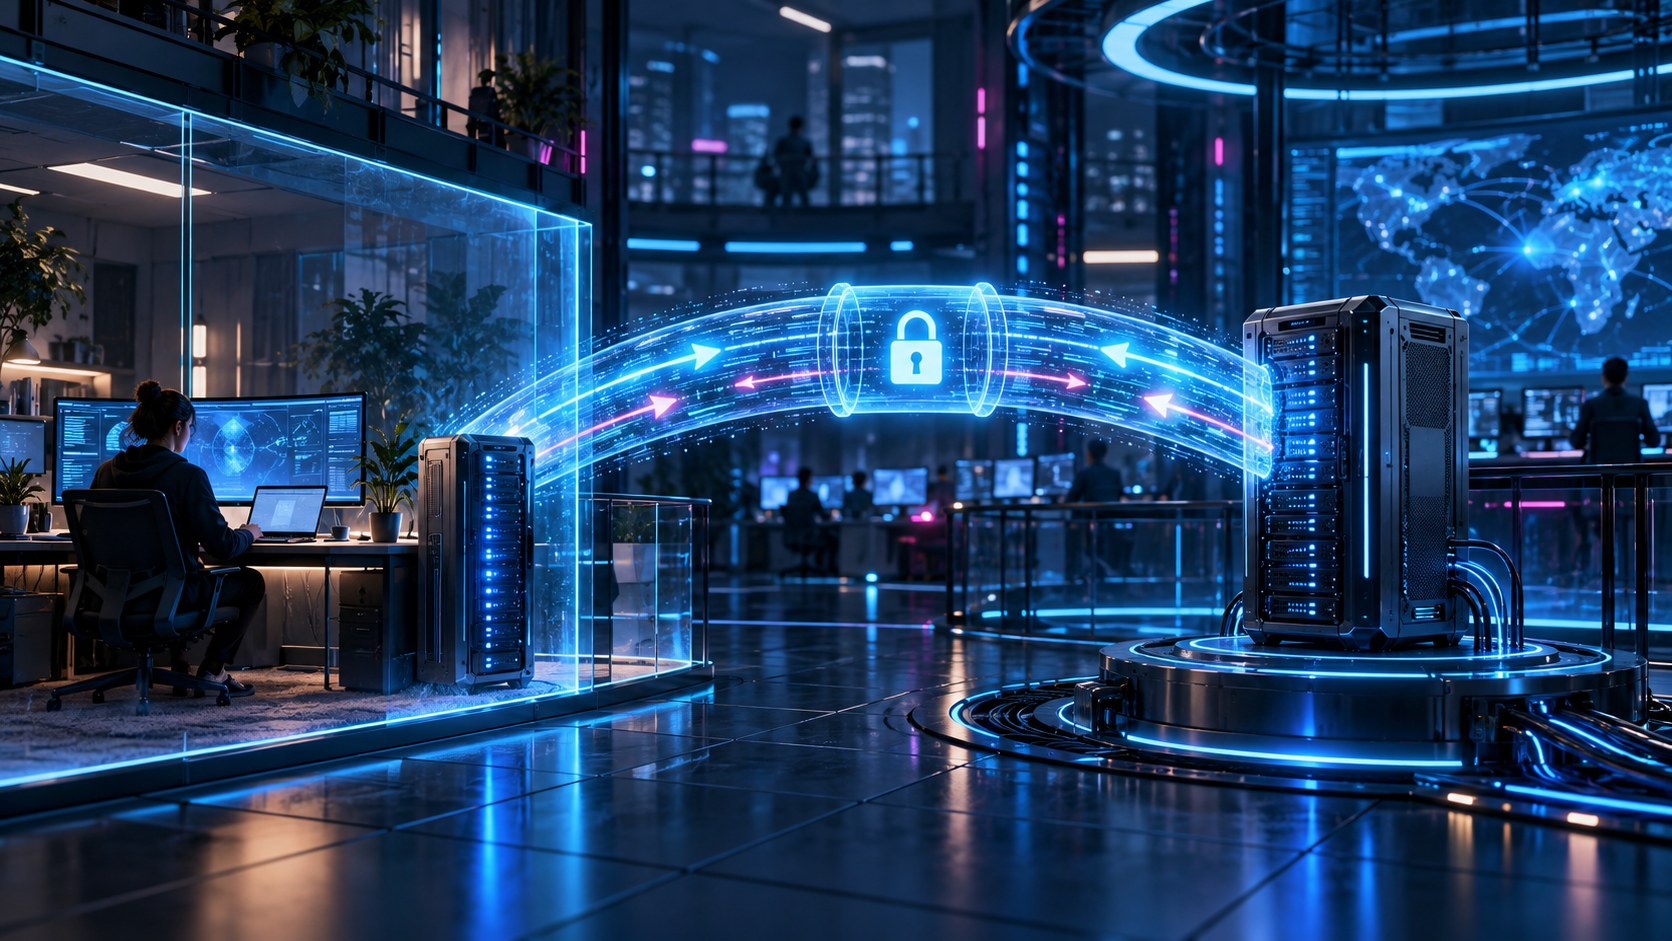
Build and troubleshoot a loopback-bound reverse SSH tunnel for private administration without exposing the forwarded service publicly.
Diagnose ADB authorization and Android connectivity, then distinguish NetHunter Rootless limitations from rooted and kernel-enabled setups.
Generate speech locally with Coqui TTS, route it into a Linux softphone microphone, and diagnose latency, echo, and missing call audio.
Introduction to the field and identifying suspicious events, tooling, and checks.
A practical tour of Windows Registry concepts and hives.
Notes on credential access, weaponizing PowerShell, and local privilege escalation.
Understanding client-side sinks and defenses for DOM-based XSS.
Linux firewall foundations with examples and common rules.
From PE format and strings to sandboxing and indicators.
Bare-metal iDRAC controller and VMware ESXi hypervisor installation.
Sessions, processes, and services explained with real OS behavior.
LAN vs WAN, addressing, DNS, TCP/UDP, NAT, and more.